We turn rapid technology change into business advantage while mitigating risk.
Helping you move from experimentation to adoption with clear governance, safeguards, compliance, and documented practices to protect your data and information.
Starting with clear rules and visible ownership, Symphonic enables your AI and digital transformation with your operational resilience in mind. We consider your whole environment so your team can manage risks, control costs, and maximise the value of your technology investments.

Most AI governance models stop at ethics and compliance. Symphonic goes further through our layered approach covering the following:
Executive visibility
Helping leaders understand AI investments, ownership, risks, performance, and business value.
Management control
Creating clearer rules, responsibilities, approval pathways, platform guidance, financial visibility, and governance structures.
Operational confidence
Making sure AI-enabled tools, workflows, and solutions can be monitored, supported, secured, restored, and improved over time.
Sustainable AI value
Connecting AI use to measurable business outcomes such as ROI, efficiency, adoption, risk reduction, compliance confidence, and growth.
This gives organisations a more complete way to govern AI, not only as a risk issue, but as a growing business capability that needs structure, discipline, and long-term stewardship.
Make technology work for the business
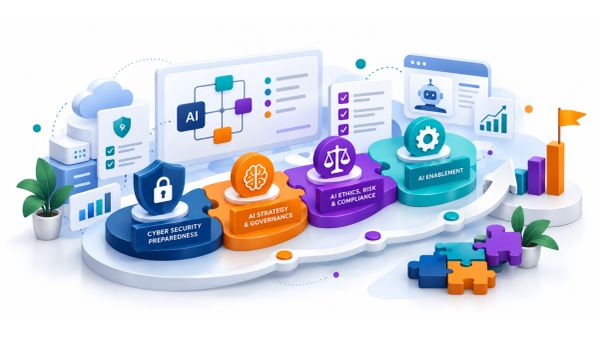
Cyber Security Preparedness
- Build the governance, controls and evidence needed to meet security expectations.
AI Strategy & Governance
- Decide where AI can create value and how it should be governed.
AI Ethics, Risk & Compliance
- Set proportionate safeguards around how AI is used.
AI Enablement
- Put AI into useful workflows and help teams adopt it effectively.
Implementation and Remediation Support
- Structured action plans, work packages, process improvements, stakeholder coordination, and evidence preparation.
Audit and Certification Readiness
- Preparation for internal review, external audit, certification, or compliance assurance through stronger documentation and evidence.
AI-Integrated Security Governance
- Alignment across AI governance, information security, risk management, accountability, and responsible AI use.
AI Cost, ROI, and Value Realisation
- Track AI spend, subscriptions, token usage, adoption, and measurable business value to support better investment decisions.
AI Operations, Monitoring, and Resilience
- Set up the monitoring, support, security, backup, restore, and review processes needed to keep AI-enabled work reliable.
AI Training and Responsible Adoption Support
- Equip leaders and teams with the practical guidance they need to use AI responsibly within the organisation’s governance structure.
Baseline cyber security maturity guidance for reducing common cyber risks through assessment, prioritisation, remediation planning, and implementation coordination.
A trust-based control framework focused on security, availability, processing integrity, confidentiality, and privacy. We support readiness and control alignment to help organisations prepare for assurance activities.
An Information Security Management System standard focused on structured security governance and control maturity. We support ISMS maturity, risk assessment, Statement of Applicability, policy uplift, remediation planning, and certification readiness.
An Artificial Intelligence Management System standard for responsible AI governance and risk management. We support alignment across AI use, accountability, impact assessment, information security governance, and broader governance integration.
Risk management guidance for identifying, assessing, treating, and monitoring organisational risk. We help connect cyber and information security risks with broader risk management practices.
An APRA prudential standard focused on operational risk management and resilience. We support alignment across governance, third-party dependencies, business continuity, and control structures.
An APRA prudential standard focused on information security capability and control effectiveness. We support information security control review, cyber risk alignment, incident response readiness, and policy uplift.
AI & Digital Enablement in Practice
See how Symphonic has helped organisations strengthen governance, manage technology risk and turn AI and digital priorities into practical action.
Ready to explore or scale your digital business?
Stay compliant. Stay resilient. Grow with confidence. With the right structure and expertise, we can help you orchestrate success.