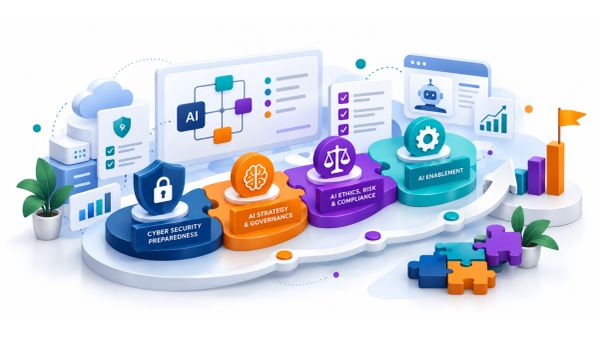
Most AI governance models stop at ethics and compliance. Symphonic goes further through our layered approach covering the following:
Executive visibility
Helping leaders understand AI investments, ownership, risks, performance, and business value.
Management control
Creating clearer rules, responsibilities, approval pathways, platform guidance, financial visibility, and governance structures.
Operational confidence
Making sure AI-enabled tools, workflows, and solutions can be monitored, supported, secured, restored, and improved over time.
Sustainable AI value
Connecting AI use to measurable business outcomes such as ROI, efficiency, adoption, risk reduction, compliance confidence, and growth.
This gives organisations a more complete way to govern AI, not only as a risk issue, but as a growing business capability that needs structure, discipline, and long-term stewardship.
Cyber security maturity guidance for reducing common risks.
Control framework for security, availability, confidentiality, privacy and assurance readiness.
Information security management standard for governance, risk and control maturity.
AI management standard for responsible governance, risk and accountability.
Risk management guidance for identifying, assessing and treating organisational risk.
Operational risk and resilience standard covering continuity, third parties and controls.
Information security standard focused on cyber capability, controls and incident readiness.
AI & Digital Enablement in Practice
See how Symphonic has helped organisations strengthen governance, manage technology risk and turn AI and digital priorities into practical action.